Site-to-site
Connect LAN networks behind two private gateways.
A site-to-site policy routes traffic between LAN networks that sit behind two different gateways, over the gateways’ WireGuard tunnel. Use it to connect an office subnet to a datacenter subnet. It does not grant endpoint users access to services; that stays with access policies.
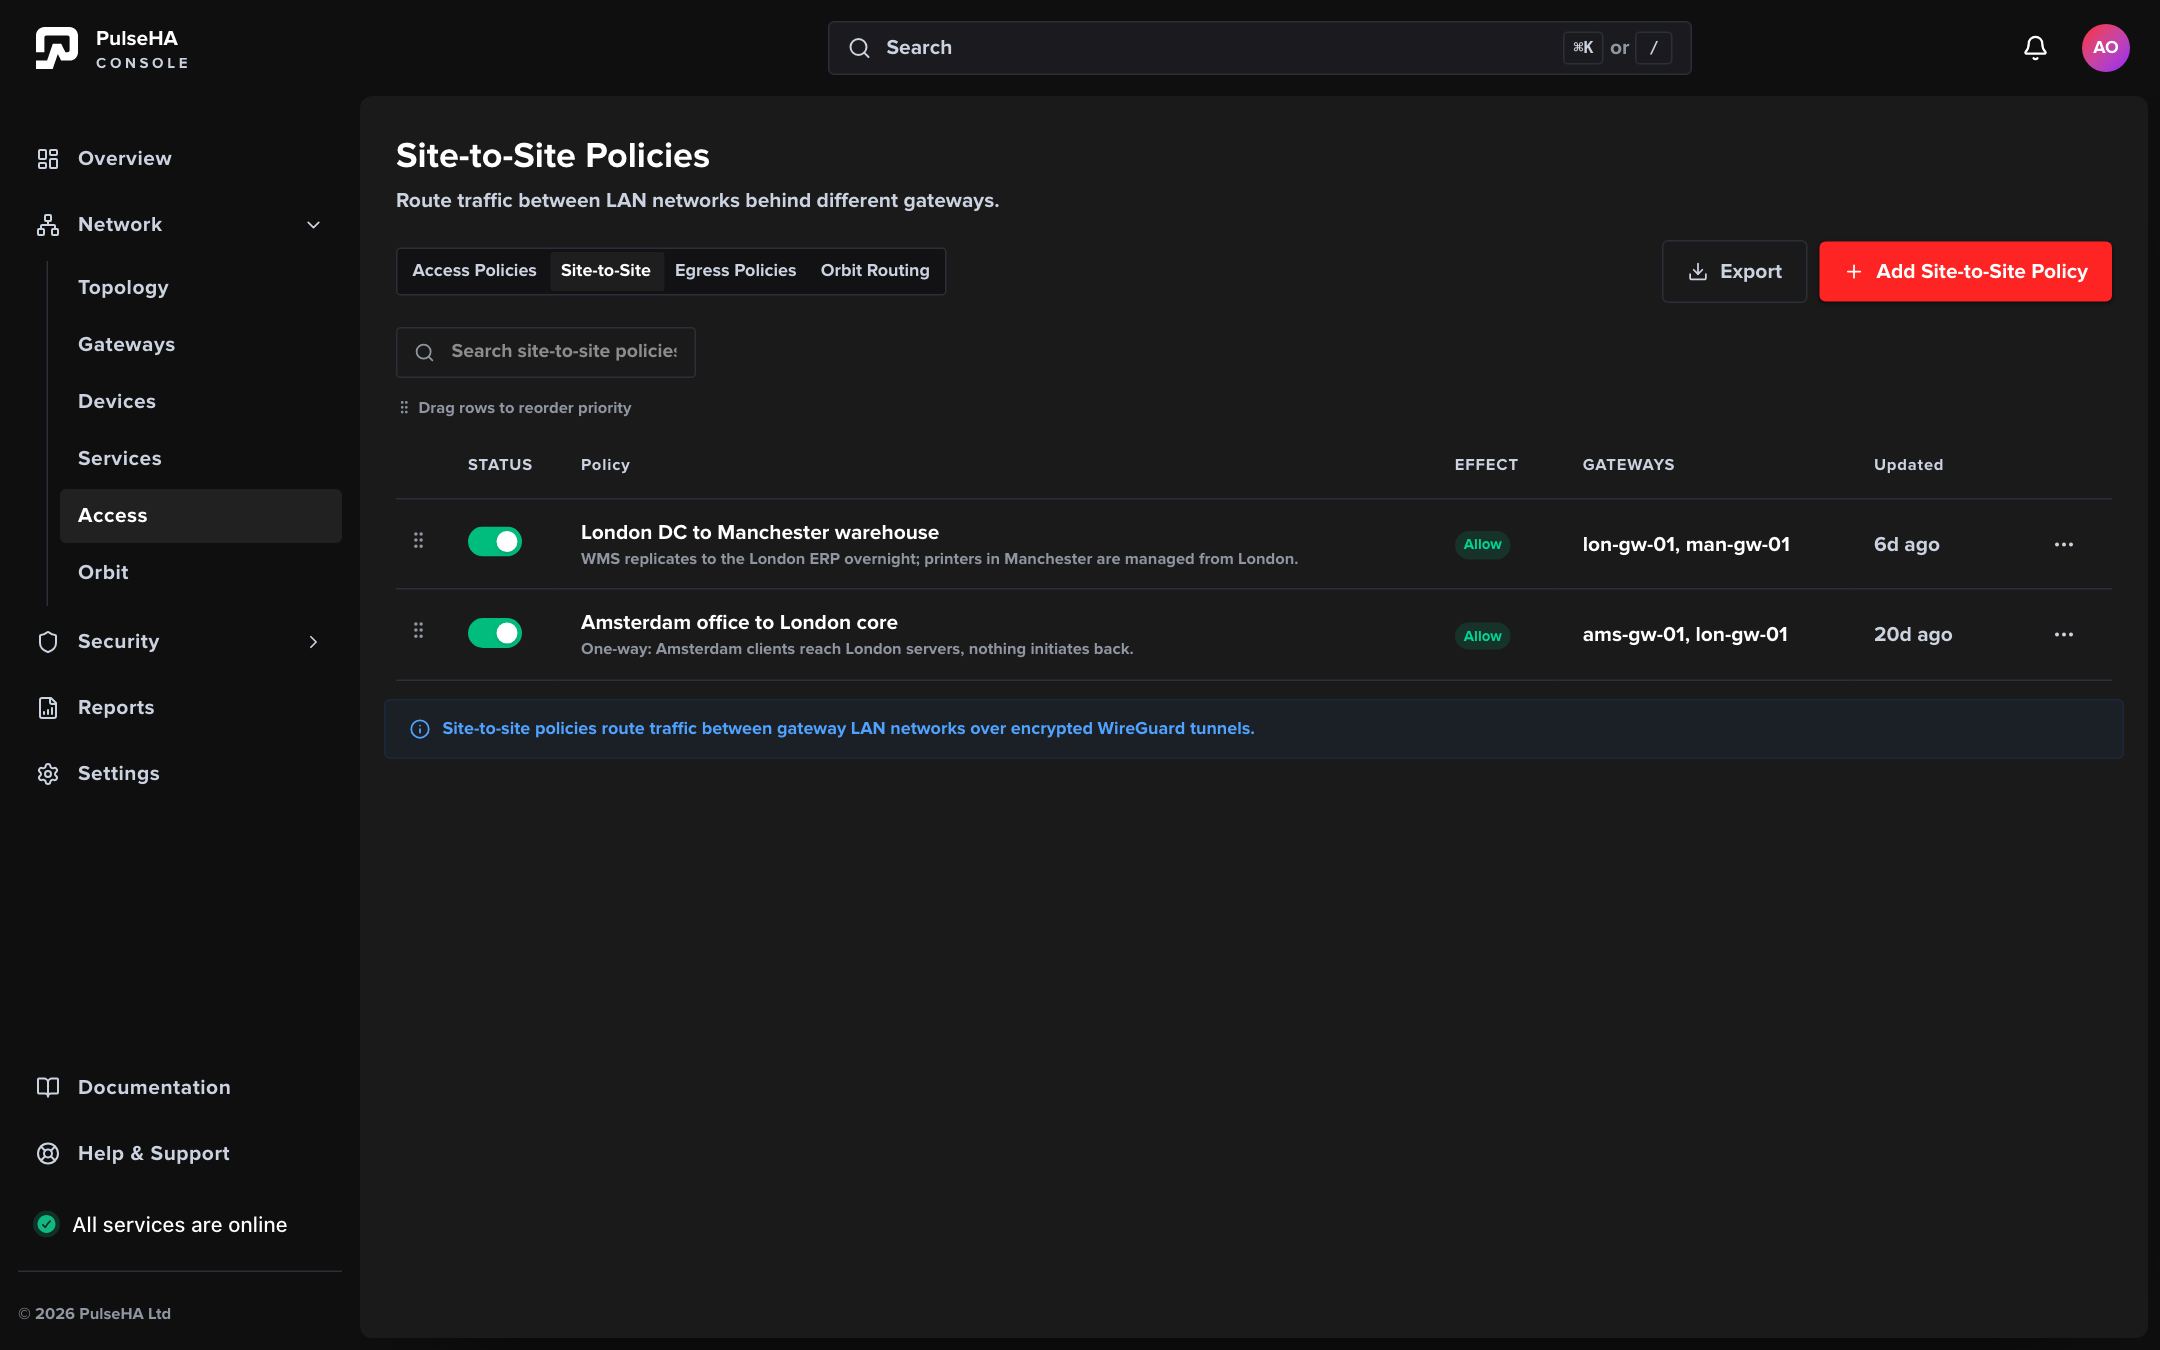
Each policy names the two gateways it connects; the Effect column shows Allow or Deny and the switch enables or disables the route.
Before you start#
- Policies live under Network → Access on the Site-to-Site tab. Creating needs
policies:create, editing and toggling needpolicies:update, deleting needspolicies:delete. - Both gateways must exist and each must have at least one Enabled LAN network declared on its Networks tab (see Gateways). Adding networks needs
gateways:update. The form says No networks configured on this gateway. Add LAN networks on the gateway detail page first. until you do. - Source and destination must be different gateways.
- This release routes all protocols and all ports. The Protocol and Port fields are shown disabled with the note Only all protocols and ports are supported.
Create a route#
- Open Network → Access, switch to Site-to-Site and click Add Site-to-Site Policy.
- Under Basic Information enter a Policy Name, choose Allow or Deny, set Priority (lower number wins) and tick Bidirectional (both sides can initiate) and Enabled as needed. Bidirectional is on by default.
- Under Source pick the Gateway, then one or more of its Networks. Only enabled networks are listed.
- Under Destination pick the other Gateway and its Networks.
- Click Create Policy. You return to the Site-to-Site tab.
Validation stops the save with Policy name is required, Select a source gateway, Select at least one source network, Select a destination gateway, Select at least one destination network or Source and destination gateways must be different. If the network lists could not be fetched you see Network data could not be loaded. Reload before saving.
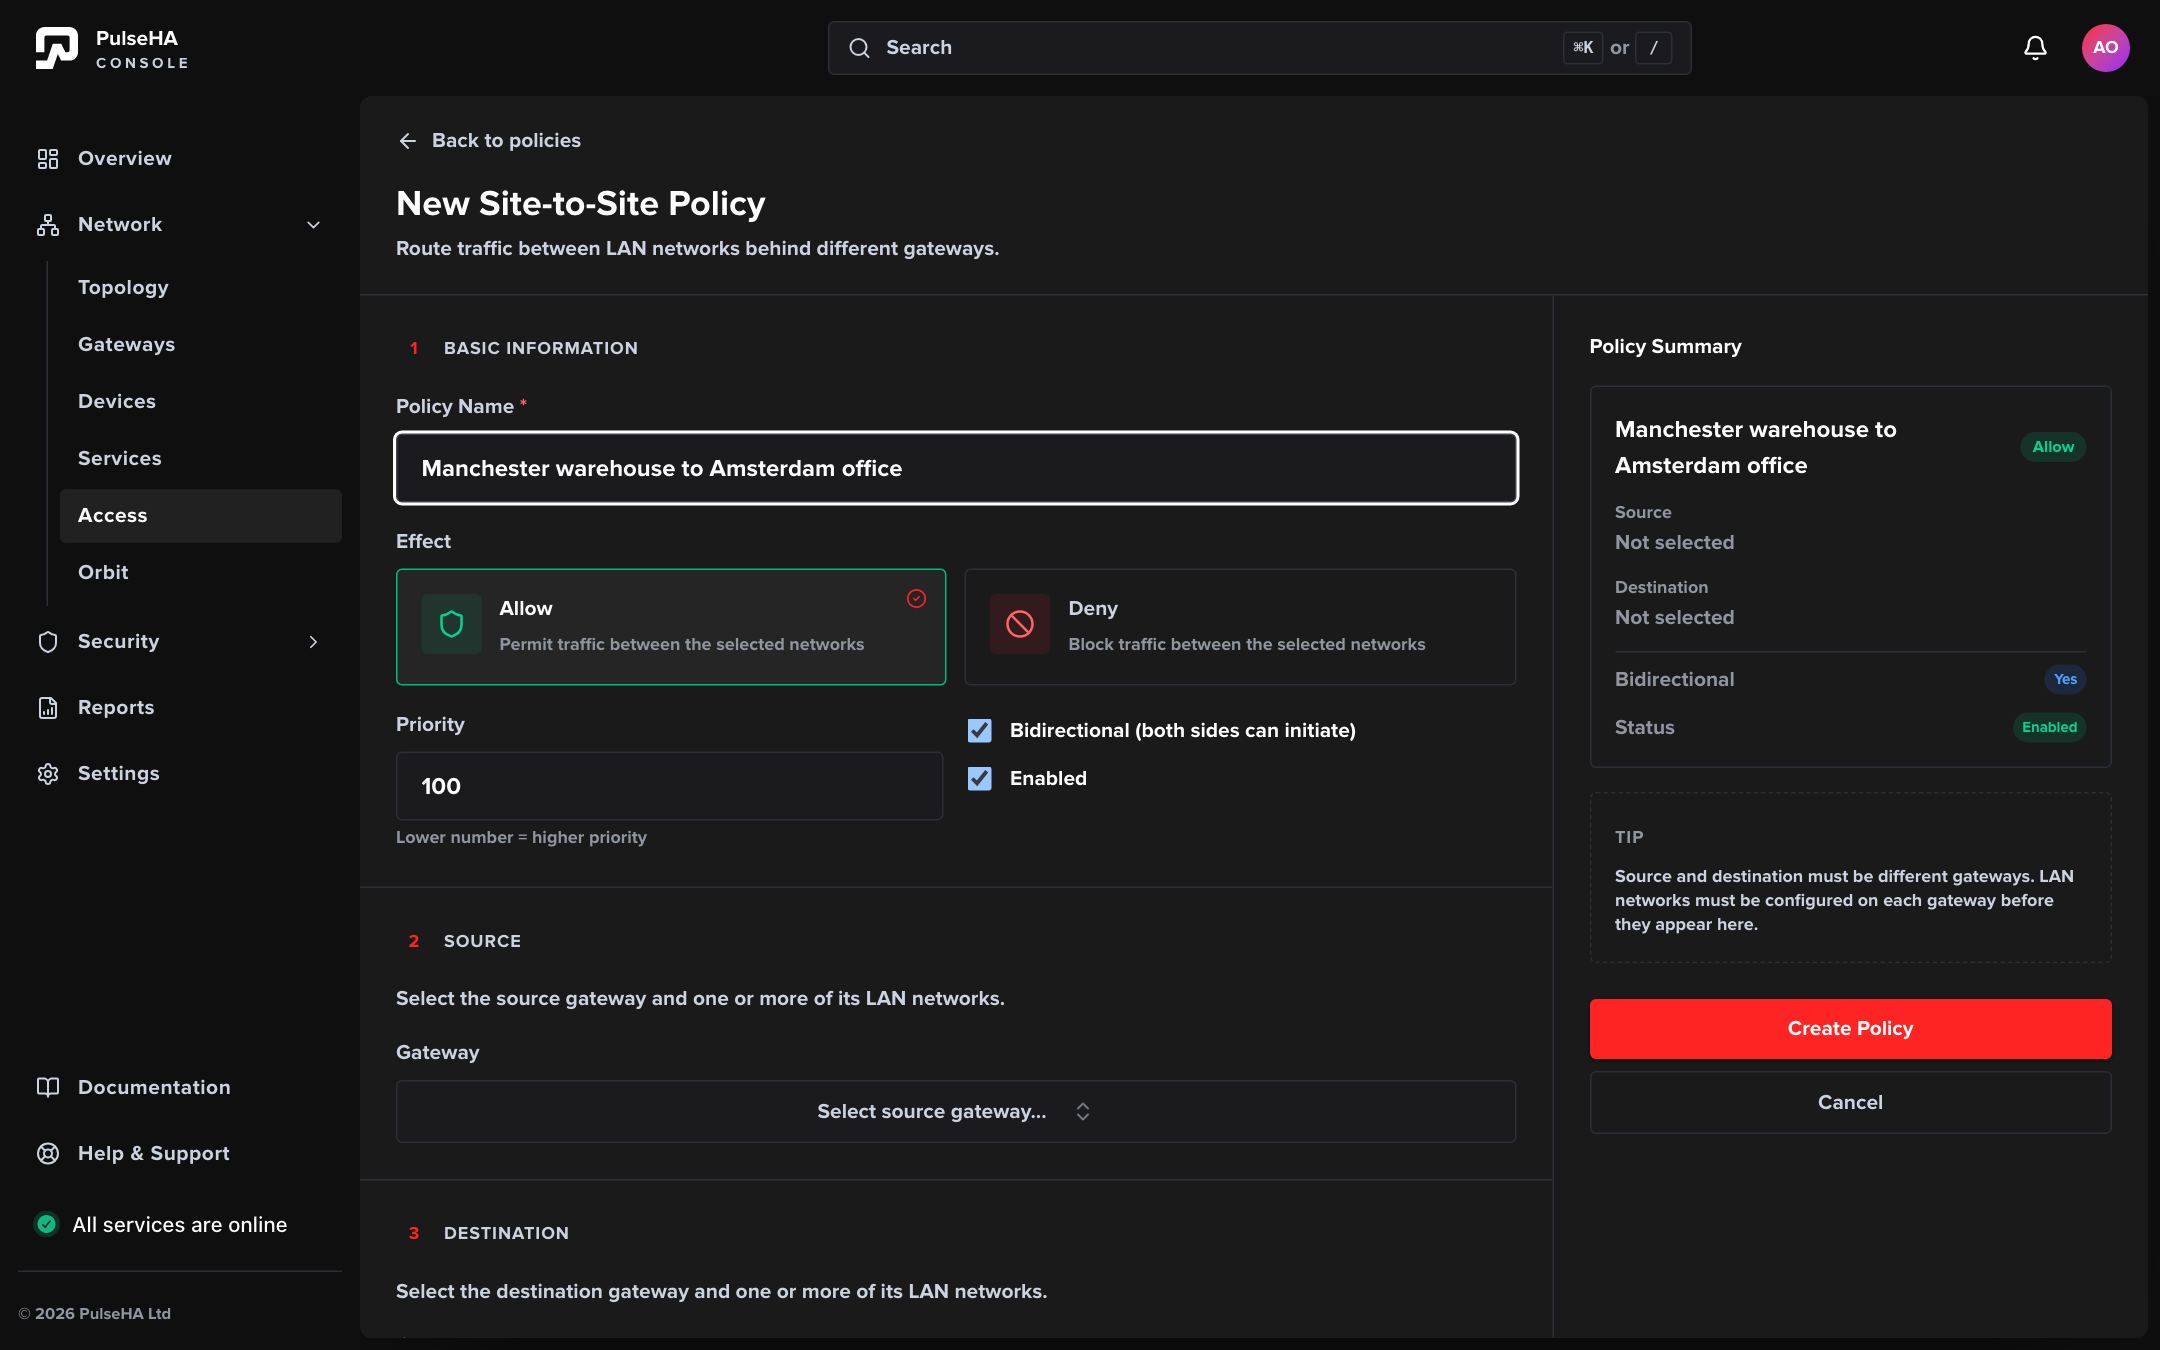
Source and destination each take a gateway and one or more of its enabled networks; protocol and port are fixed to all.
What the gateways receive#
When a site-to-site policy is enabled, the control plane adds each gateway as a WireGuard peer of the other and builds routes from the networks:
- The source gateway learns routes to the destination networks and a forward rule allowing traffic from its local source networks to them.
- The destination gateway learns the source networks as return routes and a forward rule allowing inbound traffic from them to its local destination networks. Replies are covered by connection tracking.
- With Bidirectional on, both gateways also get the reverse forward rules, so hosts on either side can open connections.
- A network’s Masquerade flag applies source NAT to traffic entering that network, so remote hosts appear as the gateway’s LAN address.
- A Deny policy produces deny rules for the same pairs, carrying the policy’s Priority so the gateway can order them against allow rules.
Disabled networks and disabled policies are ignored. Policies with stored conditions block publication for that gateway, which is why the form offers none.
Read the list#
| Column | Meaning |
|---|---|
| Status | Enabled switch (or Enabled / Disabled chip without update rights) |
| Policy | Name and notes |
| Effect | Allow or Deny |
| Gateways | The two gateways involved |
| Updated | Last change |
Row actions are Edit policy and Delete policy. Deleting warns This will remove routing between the connected networks. Drag rows to reorder when sorted by priority without a search.
Troubleshooting#
- Hosts cannot reach the remote subnet. Confirm the policy is Enabled, both networks are Enabled on their gateways, both gateways are Online, and the LAN hosts route the remote CIDR via the gateway. Check whether an enabled Deny policy covers the same pair.
- Only one direction works. Bidirectional is off. Edit the policy and tick it, or add a second policy in the other direction.
- Remote hosts see the wrong source address. Turn Masquerade on or off for the entered network on the gateway’s Networks tab; the flag applies to traffic entering that network.
- The gateway drop-down lists a gateway but its Networks box is empty. No enabled network exists on that gateway. Add one and reload the form.
- The simulator says Site-to-Site is N/A. Expected. The simulator evaluates endpoint-to-service access and does not evaluate site-to-site routes.